Generation 2 & Trusted launch
Bring existing VMs up to the current security generation
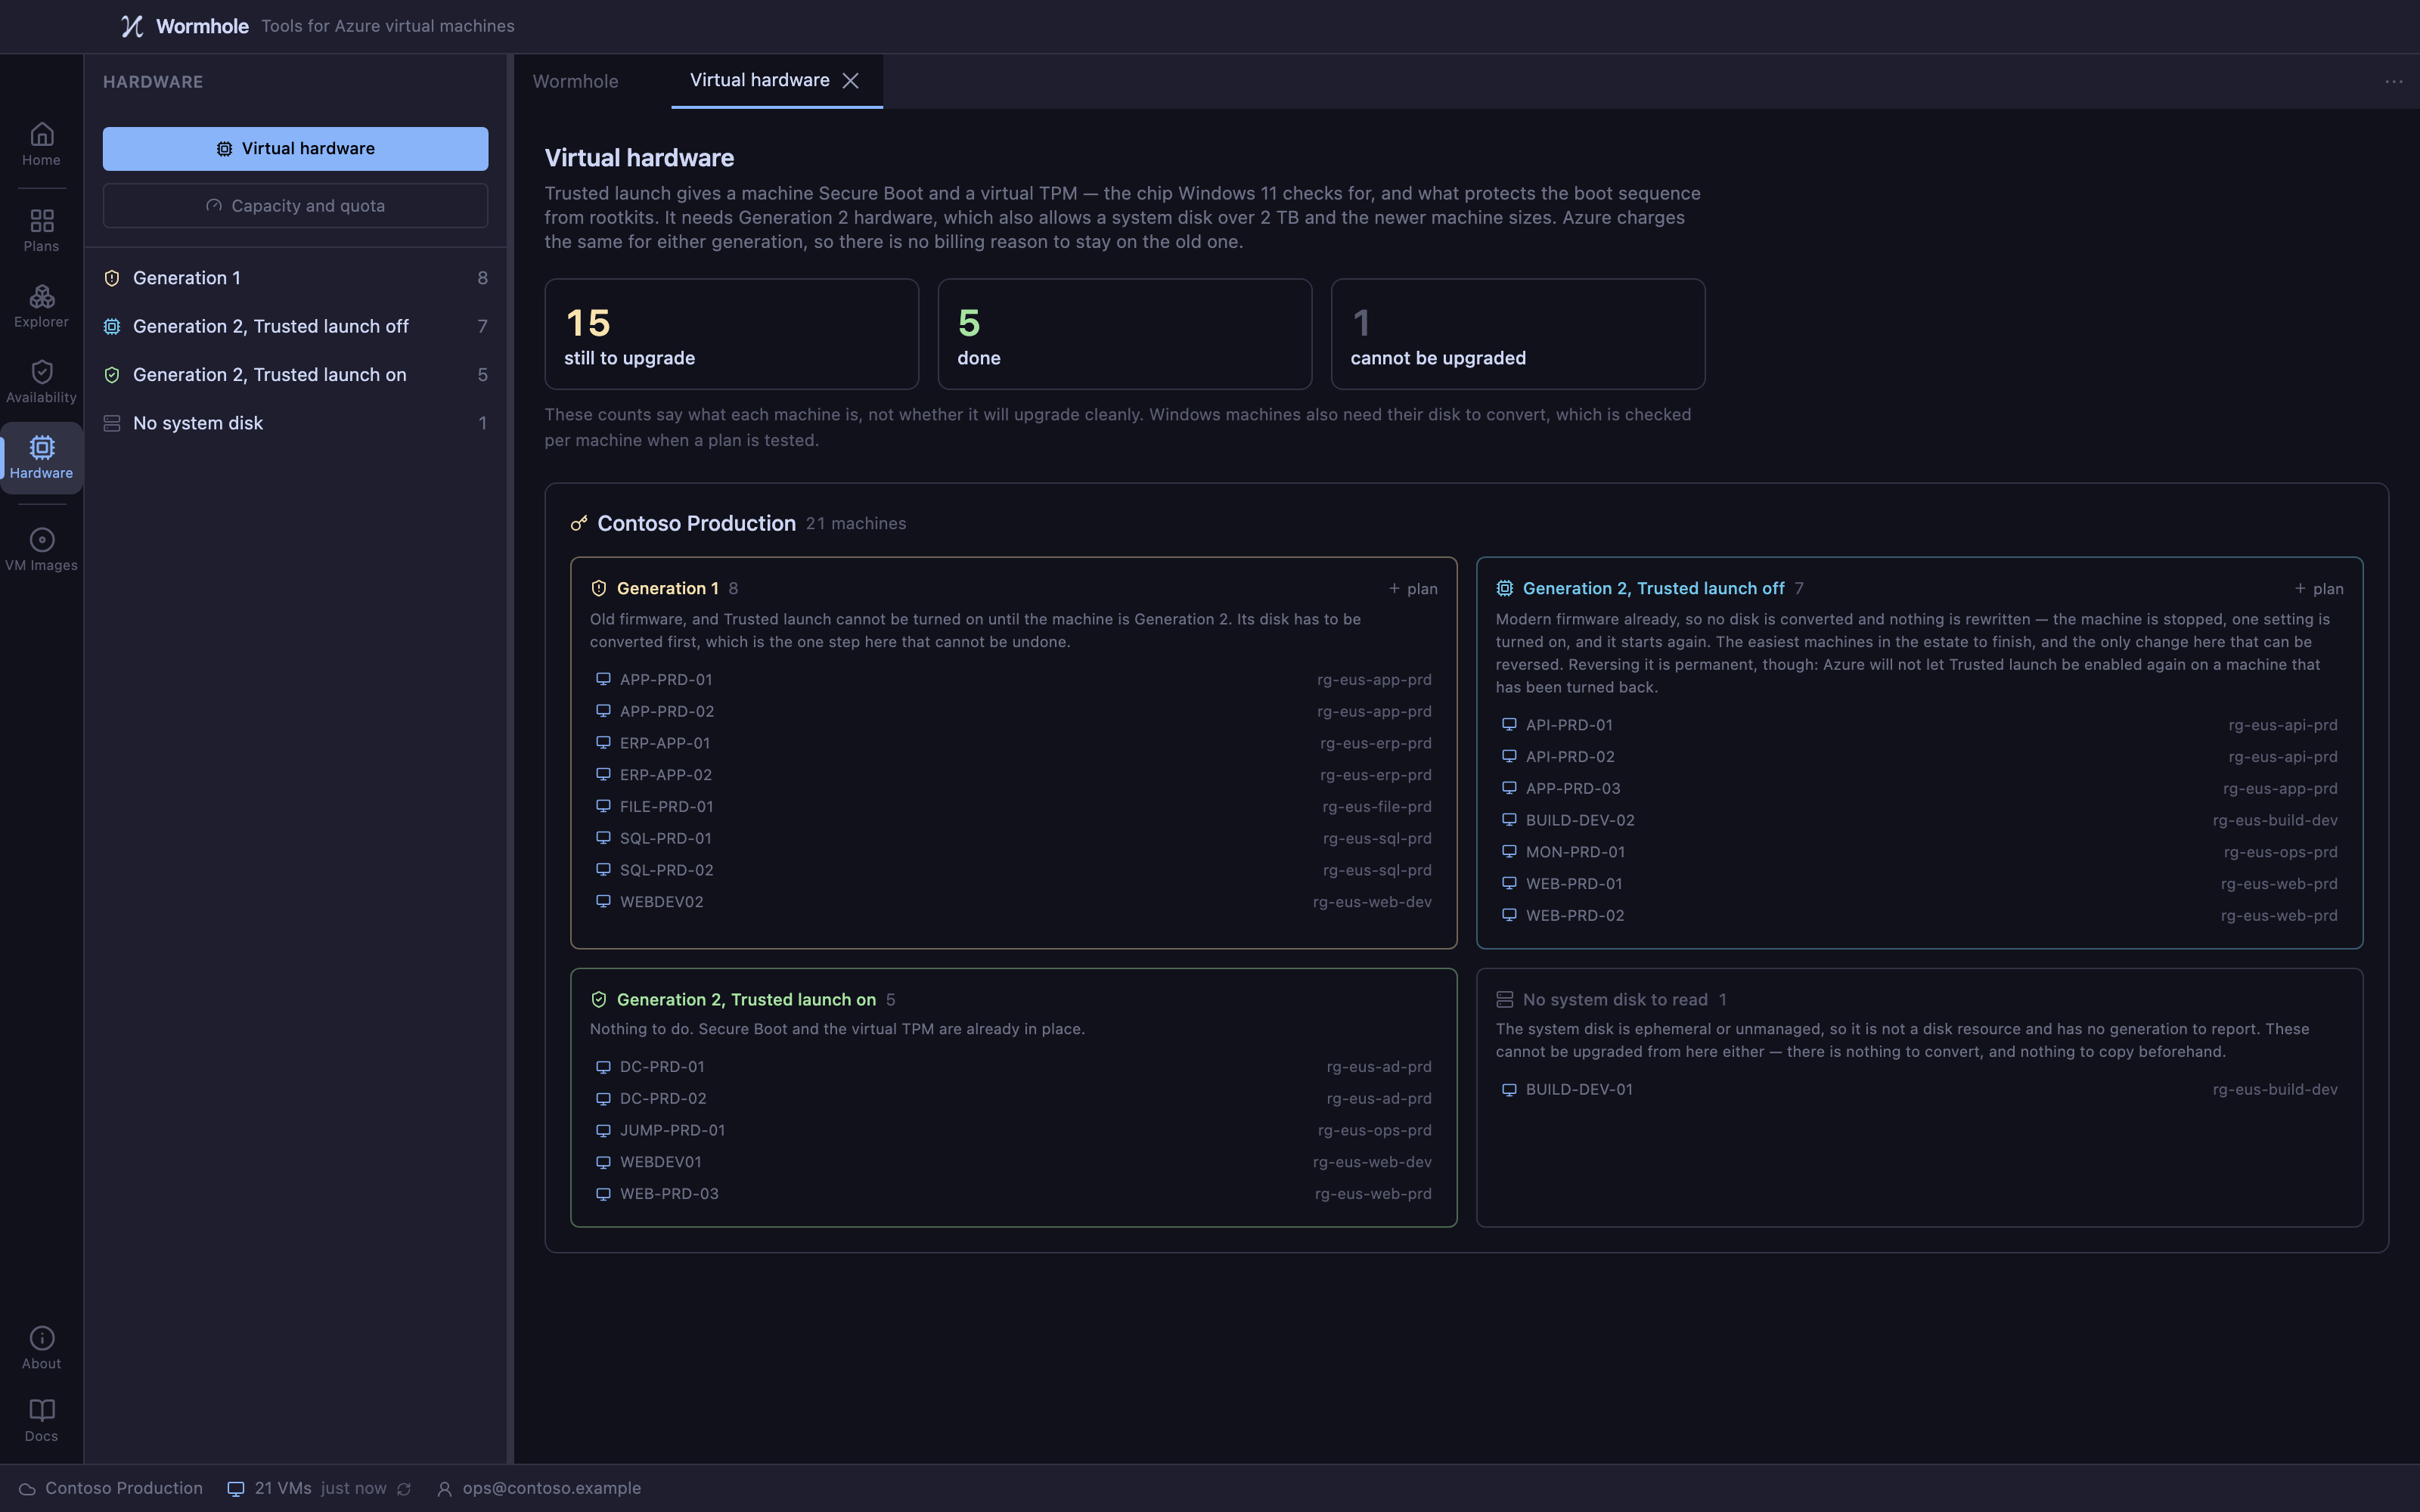
Wormhole raises Generation 1 machines to Generation 2 with Trusted launch, and turns Trusted launch on for machines already on Generation 2, across an estate rather than one machine at a time.
What Trusted launch gives a machine
Secure Boot means the machine only boots software signed by a trusted publisher. A virtual TPM is the security chip Windows 11 requires.
Generation 2 is the newer firmware. It also allows system disks over 2 TB and the newer machine sizes. Azure offers Generation 2 conversion and Trusted launch only together, so Wormhole does them together.
Generation 1 → Generation 2
Rewrites the system disk so it can boot the newer firmware, then switches the machine to Generation 2 with Trusted launch on.
- Check
- Ask the machine
- Copy disk
- Convert
- Switch firmware
- Start
A copy of the disk is taken before conversion, and is the way back. Converting the disk is the point of no return, and it is never run twice: if a run is interrupted and Wormhole can't tell from its record whether conversion finished, it says so rather than guessing.
Trusted launch on Generation 2
For machines already on Generation 2. One setting changes. Nothing is copied and nothing is rebuilt.
- Check
- Stop
- Turn on
- Start
No point of no return: Azure will remove the setting again on request. A machine is only reported finished after Wormhole has read it back and found it running with Trusted launch on.
It asks the machine first
Secure Boot refuses kernel modules that aren't signed, so a Linux machine running a custom kernel or locally built drivers can take the change and then fail to boot. Both operations that turn Secure Boot on ask the machine first, and warn rather than refuse.
Assessment reports whether each machine's generation can be raised before anything is changed, and a plan only offers machines that need the operation it does.
If a run is interrupted
Every step is recorded as it happens. Continue finishes the machines from the record. Recover puts them back: a converted machine is rebuilt on the copy of its disk taken before, and a Trusted launch change is turned back off.
Where Wormhole can't tell what state a machine is in, it changes nothing and says why.
Raising an estate to Trusted launch?
Wormhole hasn't been released yet. Tell us about your estate and we'll let you know when it is.